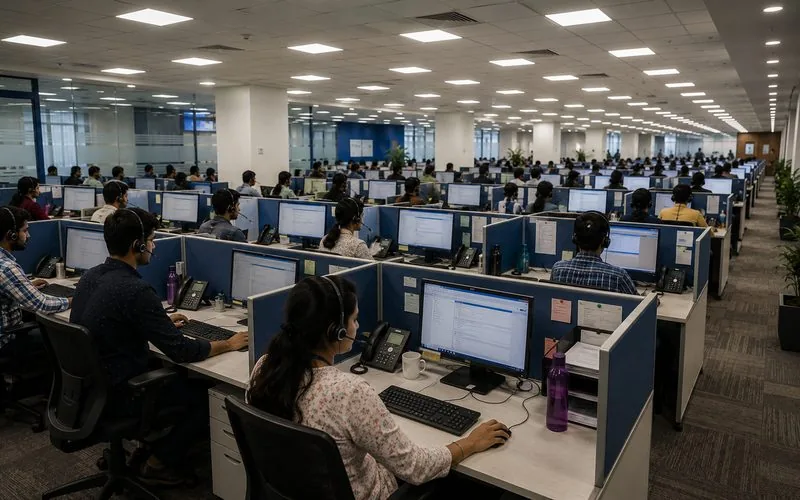
PrivAce Technologies retires agent desktops, thin clients, laptops, servers and recording systems for BPOs and contact centres across India. Drives are wiped or destroyed with erasure reports and certificates for client audits, and working equipment is bought back with payment before pickup.
What is at stake
Why disposal needs care here.
Contact centres process customer names, phone numbers, account details and, in many processes, payment card data. Call recording servers and agent machines keep it long after a campaign ends.
Client audits usually ask for device-level proof of destruction, and card-handling processes fall under PCI DSS, which requires media with cardholder data to be destroyed or made unrecoverable when no longer needed.
Rules that apply
The requirements behind a disposal policy.
Plain summaries with links to the source. Your legal and compliance teams decide how they apply to you.
PCI DSS v4.0, requirement 9.4.7: Electronic media with cardholder data must be destroyed, or the data made unrecoverable, when it is no longer needed.
Digital Personal Data Protection Act, 2023 and DPDP Rules, 2025: Personal data on a retired device is still your responsibility. Failing to take reasonable security safeguards can attract a penalty of up to ₹250 crore. Most obligations apply from 13 May 2027.
ISO/IEC 27001:2022, controls 7.14 and 8.10: Control 7.14 covers secure disposal or reuse of equipment, and 8.10 covers deletion of information. Certified organisations need evidence for both.
What we do
How we handle it for you.
High-volume desktop and thin client retirement, floor by floor
Recording server and storage decommissioning with drive-level certificates
Certificates grouped by client process for audits
Weekend and night pickups to avoid disrupting shifts
Questions
Questions, answered.
Yes. Pickups and onsite destruction can be scheduled at night or over weekends.
Many thin clients have small flash storage with configuration and cached credentials. We wipe or destroy it like any other media.
Yes. Tag devices by process and the certificates follow the same grouping.
Requirement 9.4.7 of PCI DSS v4.0 requires electronic media with cardholder data to be destroyed, or the data rendered unrecoverable, when it is no longer needed.